Practical technical articles by Fahad Bin Shakir on newsroom architecture, WordPress, web security, DevOps, performance, multilingual publishing, and production delivery. These authored resources are separate from the portfolio assistant and advertising surfaces.
WordPress & CMS
Architecture, publishing workflows, deployment, debugging, and safer CMS operations.
WordPress Architecture · 15 min read
A decision framework for shared newsroom platforms covering tenancy, editorial roles, releases, media, search, failure isolation, and operational ownership.
WordPress Security · 11 min read
A defence-in-depth approach to WordPress media uploads covering validation, storage, execution controls, authorization, observability, and incident response.
DevOps · 12 min read
A release workflow for WordPress code, configuration, database changes, media, rollback, verification, and operational ownership.
Production Debugging · 11 min read
A layered method for diagnosing WordPress outbound request failures across application code, DNS, TLS, proxies, firewalls, and remote APIs.
DevOps
Repeatable releases, infrastructure baselines, migrations, verification, and recovery planning.
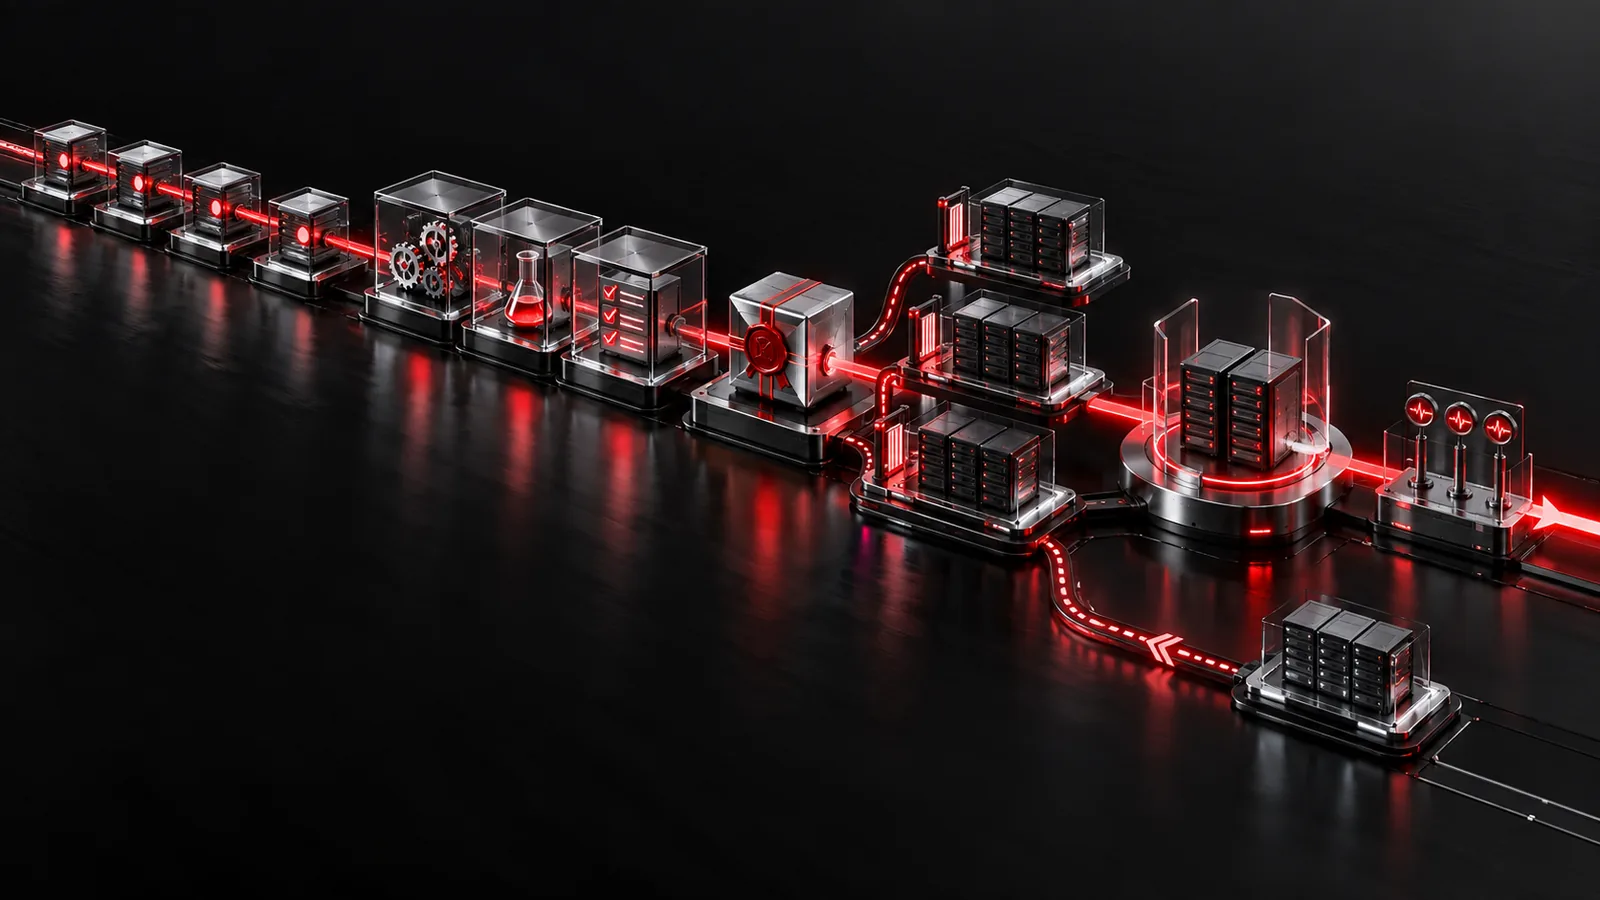
DevOps · 14 min read
A release pipeline design that turns a reviewed commit into a traceable artifact, controlled deployment, observable verification, and rehearsed rollback.
DevOps · 13 min read
A staged migration method covering inventory, URL mapping, data integrity, DNS, redirects, observability, rollback, and search continuity.
Cybersecurity
Practical application, server, browser, and form protections for production systems.
Web Security · 14 min read
How to keep one complete Content Security Policy authoritative while applications, proxies, hosting panels, and CDNs all participate in the response path.
Infrastructure Security · 12 min read
A maintainable baseline for identity, patching, network exposure, service isolation, secrets, logging, backups, and recovery on a small production server.
Web Security · 12 min read
How TLS, canonical redirects, HSTS, CSP, framing, MIME, referrer, and permissions policies work together without breaking the application.
Application Security · 11 min read
A contact-form architecture covering browser UX, server validation, abuse controls, origin checks, email delivery, privacy, logging, and truthful failure states.
SEO & Analytics
Crawlability, canonical signals, structured data, measurement, and production SEO checks.
Technical SEO · 12 min read
A production-first audit method for crawl access, status codes, canonicals, rendering, sitemaps, structured data, internal links, and legacy URL cleanup.